

Every day, you send messages, shop online, and check your bank balance on your phone. Behind the scenes, secret math keeps your private details safe from hackers. Today, people worry more than ever about their digital safety. According to a Pew Research Center study, 81% of consumers believe companies use their personal data in ways that make them feel uncomfortable.
Furthermore, a survey from the Identity Theft Resource Center shows that 80% of consumers received a data breach notice in the past year, and 50% fear immediate money fraud after a leak. Because of these real risks, strong data locking tools are vital. One of the best tools protecting your daily life is the block cipher. In this simple guide, you will learn what a block cipher is and how it works.
What Is A Block Cipher?
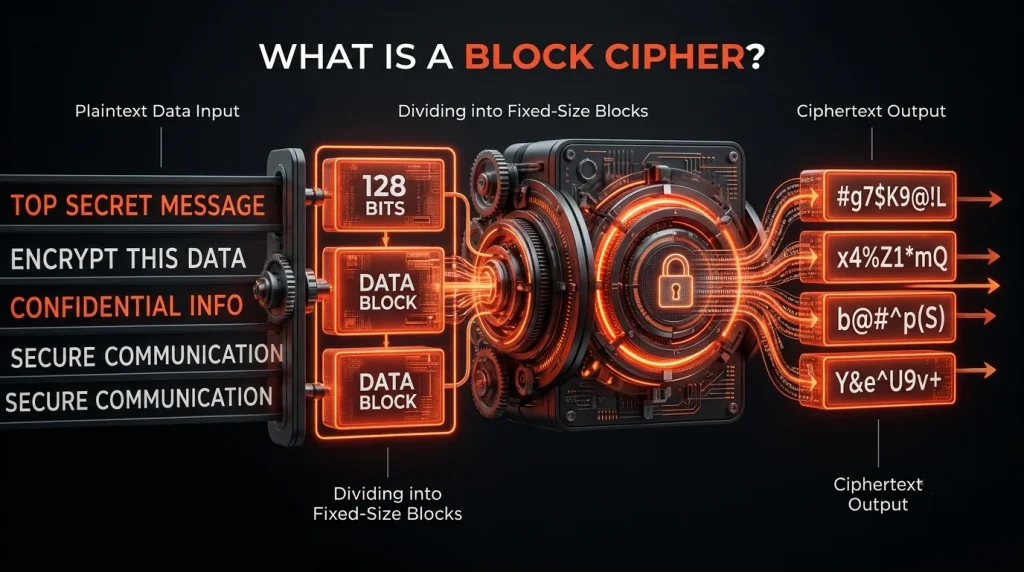
To understand what a block cipher is, you first need to understand a simple idea called encryption. Encryption is the process of taking normal, readable information and turning it into a secret, scrambled code so that strangers cannot read it. When you type your credit card number into a shopping website or save a private file on your laptop, your device scrambles that information. Only someone who has the right secret key can unlock the code and read the original words.
A block cipher is one of the most popular ways computers lock and unlock digital data. Instead of scrambling your message one single letter or one tiny bit at a time, a block cipher cuts your data into equal, fixed-size chunks called blocks. Then, it locks each block one whole chunk at a time using a shared secret key and a list of math steps.
You can think of a block cipher like packing a long letter into identical metal lockboxes before mailing it to a friend: Imagine you write a long secret letter, and you want to mail it without anyone else reading a single word. You buy a stack of small metal boxes. Every box is built to hold the exact same amount of paper, such as 16 letters per box. You cut your long letter into neat strips of 16 letters each and place one strip into each box.
Inside every box, a small machine mixes up the order of those 16 letters and swaps them with code symbols based on a secret key. You close the boxes and send them in the mail. If a thief steals a box on the way, all they see is a jumble of random symbols. When your friend receives the boxes, they use an exact copy of your secret key to run the machine in reverse, putting the 16 letters in each box back into their normal order.
Because both the person sending the message and the person receiving the message use the exact same secret key to lock and unlock the boxes, a block cipher is part of a family called symmetric encryption. The word symmetric simply means that both sides use the same key.
The 6 Main Parts Of A Block Cipher
Before we walk through how a block cipher scrambles data from start to finish, it helps to learn the six basic parts involved in the process. Each part has one clear, simple job.
1. Plaintext (The Original Readable Data)
Plaintext is your normal, unlocked information before the block cipher touches it. In everyday life, plaintext can be a text message to your family, a password, a bank transfer, a voice recording, or a photo. To a computer, all plaintext is stored as a long line of ones and zeros, which are called bits.
2. Block Size (The Size of Each Box)
Every block cipher is built to handle a strict, fixed block size measured in bits. A cipher will never change its box size in the middle of a job. Older block ciphers usually worked with a 64-bit block size, which is enough room to hold 8 normal characters of text at a time. Modern block ciphers almost always use a 128-bit block size, which holds 16 characters of text in every single block.
3. Padding (Packing Peanuts for Empty Space)
In the real world, your messages and files almost never divide evenly into perfect blocks. Suppose your block cipher uses boxes that hold 16 letters each, and you want to lock a short message that is 20 letters long. The first box will hold 16 letters and be completely full. However, the second box will only have 4 letters inside it, leaving space for 12 letters empty.
A block cipher cannot lock a partly empty box. To fix this problem, the computer uses padding. Padding adds extra filler bits to the end of the last block until it is completely full. It works just like pouring packing peanuts into a shipping box so the item inside fits tightly. When the receiver unlocks the box later, the computer reads a small number at the end of the padding that tells it exactly how many filler bits to throw away.
4. Secret Key and Key Size
The secret key is a special piece of digital information that tells the block cipher how to mix up the data inside each block. Even if everyone in the world knows how the block cipher machine is built, nobody can unlock your data without knowing your exact secret key. Endpoint protection software helps secure devices by protecting sensitive information and defending against cyber threats.
Keys are also measured by their length in bits, such as 128 bits, 192 bits, or 256 bits. A longer key is much safer than a shorter key because it creates vastly more possible combinations, making it impossible for a hacker’s computer to guess the right key by trial and error.
5. Initialization Vector (The Starting Random Number)
Often shortened to IV, an Initialization Vector is a random block of numbers added at the very start of the locking process. Why do we need it? Suppose you send the message “Yes” to your boss on Monday, and you send the exact same message “Yes” on Tuesday using the same secret key. Without an IV, both messages would turn into the exact same scrambled code, and a snooper could guess that you gave the same answer twice. By mixing a fresh, random IV into the first block every time you send a message, the final locked code looks completely different every single time.
6. Ciphertext (The Final Scrambled Data)
Ciphertext is the locked, unreadable output that comes out of the block cipher after all the mixing steps are finished. It has the same block size as the padded plaintext, but it looks like complete nonsense to anyone who does not have the secret key.
How Does A Block Cipher Work Step By Step?
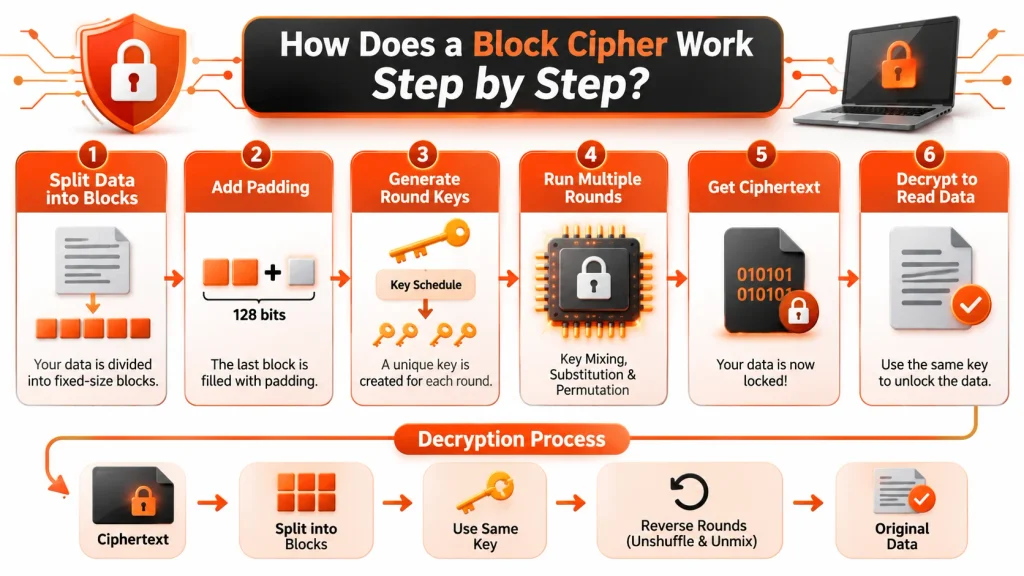
A block cipher does not just scramble your data in one single step. One quick mix would be too easy for a smart computer to solve, just like a newspaper word puzzle. Instead, a block cipher sends every block of data through an assembly line that repeats the mixing process many times. Each pass through the mixer is called a round.
Let us walk through the exact steps a block cipher takes to lock your data.
Step 1: Turning Your Data into Fixed-Size Blocks
First, your computer takes your file or message and reads it as a long stream of binary bits (ones and zeros). While antivirus software scans files for malicious code, encryption helps protect sensitive data from unauthorized access. The block cipher steps in and slices that long stream into equal pieces based on its block size. For example, if you are using a 128-bit block cipher and your message is 500 bits long, the cipher cuts the first 384 bits into three full blocks of 128 bits each, leaving 116 bits for the fourth and final block.
Step 2: Filling the Last Block with Padding
Next, the block cipher looks at that fourth block, which only has 116 bits. Because the cipher requires every block to be 128 bits long, it adds 12 bits of padding to the end of the fourth block. Now, all four blocks are the exact same size of 128 bits and are ready to enter the locking machine.
Step 3: Making Round Keys from Your Main Secret Key
Before the blocks enter the mixer, the cipher prepares the keys. If a block cipher runs 10 rounds of mixing, it does not use your main secret key in its raw form 10 times in a row. Doing that would make the cipher easier for hackers to study and break.
Instead, the cipher feeds your main secret key into a helper routine called a key schedule. The key schedule stretches, shifts, and mixes your main key to create a separate, unique mini-key for every single round. These mini-keys are called round keys (or sub-keys). If the cipher runs 10 rounds, the key schedule creates 10 different round keys.
Step 4: Running the Block Through Multiple Scrambling Rounds
Now, each 128-bit block of data enters the main encryption engine. Depending on the algorithm and key size, the block will go through anywhere from 10 to 16 rounds of heavy scrambling. Inside every single round, three simple mathematical actions happen over and over:
- Key Mixing (XOR Operation): The cipher combines the data block with the round key for that specific round. It does this using a very fast computer math rule called XOR (short for exclusive OR). XOR compares two bits at a time, one from the data block and one from the round key. If the two bits are the same (both 0 or both 1), the result is 0. If the two bits are different (one is 0 and the other is 1), the result is 1. The wonderful thing about XOR is that it is completely reversible if you have the round key, and completely impossible to guess if you do not.
- Substitution (Swapping Pieces): Next, the cipher cuts the 128-bit block into smaller bite-sized pieces, usually 8 bits (1 byte) each. It looks up each piece in a secret replacement chart called a Substitution Box, or S-box. The S-box swaps the original byte with a totally different byte. This step breaks up any math patterns in your original message.
- Permutation (Shuffling Positions): After swapping the values, the cipher shifts and moves the bits or bytes to different spots across the block. Bits that used to sit next to each other are now moved far apart. This ensures that changes in one small corner of the block spread out across the entire block.
Step 5: Producing the Final Ciphertext
Once the block finishes all of its scheduled rounds (such as 10, 12, or 14 rounds), it exits the engine as a finished block of ciphertext. All the finished ciphertext blocks are placed together in order and sent across the internet or saved onto your hard drive.
Step 6: Unlocking the Data (Decryption)
When the right person wants to read the locked message, their computer runs the exact same block cipher in reverse:
- It slices the ciphertext back into 128-bit blocks.
- It uses the shared main secret key to generate the exact same set of round keys.
- It feeds the ciphertext block through the rounds backward, starting with the final round key and ending with the first round key.
- Inside each round, it un-shuffles the positions, uses an inverse S-box to swap the bytes back to their original values, and uses XOR with the round key to undo the key mixing.
- Once all blocks are unlocked, the computer strips off the padding from the very last block and hands you back the clean, original plaintext.
Confusion, Diffusion, And Internal Designs
You might wonder why a block cipher needs both a swapping step (substitution) and a shuffling step (permutation) in every single round. Why not just swap letters once and be done?
The reason comes from two famous safety rules created by mathematician Claude Shannon, known as confusion and diffusion.
What Is Confusion?
Confusion is the practice of hiding the relationship between your secret key and the final scrambled ciphertext. If a cipher only shifted letters forward by a fixed number based on your key, a clever hacker could look at a locked message, count the letter patterns, and figure out your key in seconds. Block ciphers create strong confusion using S-boxes (substitution) alongside round key mixing. Every round tangles the math between the key and the data so deeply that even supercomputers cannot work backward to find the key. Alongside encryption, identity protection services can help people monitor for signs that their personal information has been misused.
What Is Diffusion and the Avalanche Effect?
Diffusion is the practice of spreading the influence of one single plaintext bit across as much of the ciphertext block as possible. Block ciphers create diffusion through the permutation (shuffling and mixing) steps in each round.
Because of diffusion, a good block cipher shows a powerful behavior called the avalanche effect. Think of how one tiny pebble rolling down a snowy hill can set off a massive avalanche that changes the whole side of the mountain. In a block cipher, if you change just one single bit in your original plaintext message (for example, changing “Pay Bob $100” to “Pay Bob $200”), the shuffling steps spread that tiny change into other bytes during Round 1, which spread into even more bytes in Round 2, and so on. By the time the block finishes all its rounds, roughly 50% of all the bits in the final ciphertext block will flip! This prevents hackers from making educated guesses about messages that are almost the same.
Two Blueprints for Building a Block Cipher
Engineers use two main internal designs to put confusion and diffusion together inside a block cipher:
- Feistel Network: In a Feistel cipher, the 64-bit or 128-bit block is split right down the middle into a Left half and a Right half. During Round 1, the Right half is sent through a scrambling box (called a round function) along with the Round 1 key. The scrambled result is then mixed with the Left half using XOR. Finally, the two halves swap sides so the old Right half becomes the new Left half for Round 2. The biggest benefit of a Feistel Network is that the math works the exact same way forward and backward. Engineers do not need to build a separate unlocking machine; they just run the ciphertext through the exact same steps while feeding the round keys in reverse order. Older standards like DES and Blowfish use a Feistel design.
- Substitution-Permutation Network (SPN): Instead of only scrambling half of the block in each round, an SPN cipher scrambles the entire block all at once in every round. The whole block is arranged like a small grid of bytes. In every round, the whole grid is mixed with the round key, every single byte is swapped through an S-box, the rows of the grid are shifted sideways, and the columns are mixed together with math. Because it works on the entire block in every round, SPN mixes data faster and takes fewer rounds to reach complete security. The modern king of encryption, AES, uses an SPN design.
Block Cipher Modes Of Operation Explained Simply
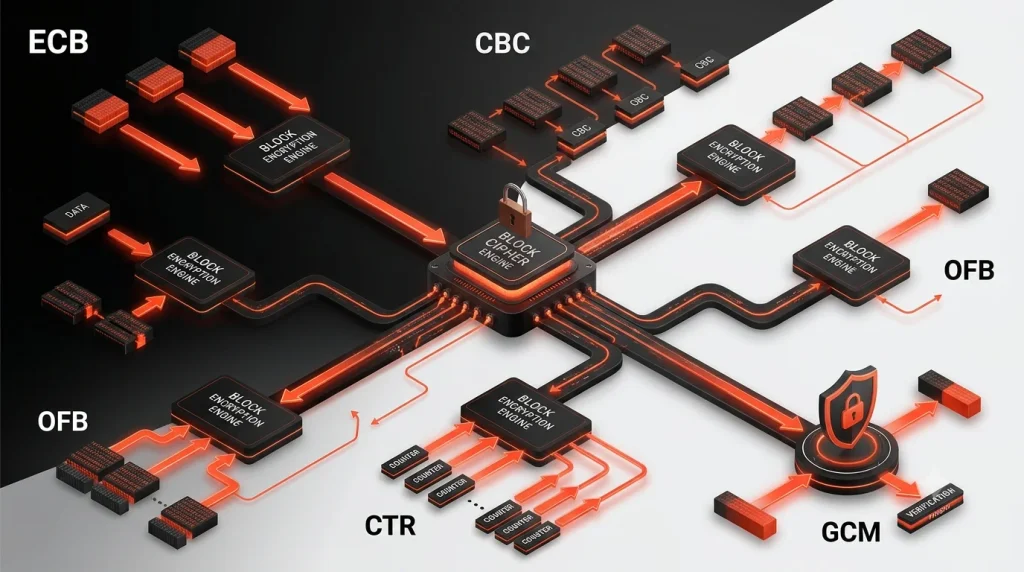
On its own, a core block cipher algorithm only knows how to lock one single block of data (such as 16 letters). What happens when you want to lock an entire movie, an email, or a 10-page document made up of thousands of blocks?
To handle messages longer than a single block, computers use a set of rules called a Block Cipher Mode of Operation. A mode of operation tells the block cipher how to connect multiple blocks together safely. Choosing the right mode is just as important as choosing a strong block cipher. A vpn for windows can use encryption modes such as AES-GCM to help protect internet traffic from unauthorized access.
1. Electronic Codebook (ECB) Mode
ECB is the most basic mode of operation. It takes your long message, cuts it into blocks, and locks every single block completely on its own using the exact same secret key.
While ECB is simple, it has a giant security problem: identical plaintext blocks always turn into identical ciphertext blocks. For example, if you use ECB mode to lock a digital image that has a large white background, every block of white pixels turns into the exact same locked block. A hacker looking at the locked file can still clearly see the shapes and outlines of the picture! Because it leaves obvious patterns behind, ECB mode should never be used to protect multi-block files or messages.
2. Cipher Block Chaining (CBC) Mode
CBC mode was invented to fix the pattern problem of ECB. As the name says, it links all the blocks together like a heavy metal chain:
- Before the very first plaintext block goes into the block cipher, it is mixed (XORed) with a random Initialization Vector (IV).
- That first block is then locked by the cipher to create Ciphertext Block 1.
- Next, Ciphertext Block 1 is mixed with Plaintext Block 2 before Plaintext Block 2 goes into the cipher!
- Ciphertext Block 2 is then mixed with Plaintext Block 3, and so on down the line.
Because every block is mixed with the locked block that came right before it, two identical blocks of words in your message will turn into completely different ciphertext blocks. The one downside of CBC is speed: because Block 2 must wait for Block 1 to finish locking, your computer cannot lock multiple blocks at the exact same time.
3. Cipher Feedback (CFB) and Output Feedback (OFB) Modes
Sometimes, a computer needs to lock data immediately as it is typed on a keyboard, rather than waiting to collect a full 16-letter block. CFB and OFB modes solve this by turning a block cipher into a tool that acts like a continuous stream cipher. Instead of putting your plaintext inside the block cipher box, the cipher locks the IV (and previous outputs) to create a secret stream of random-looking bits. That secret stream is then mixed with your plaintext bits on the fly.
4. Counter (CTR) Mode
CTR mode is one of the most popular modes used today because it is super fast. Instead of chaining blocks together one after another, CTR mode uses a starting random number (called a nonce) combined with a simple counting number: Block 1 uses counter 1, Block 2 uses counter 2, Block 3 uses counter 3, and so on.
The block cipher locks the counter number, and the resulting scrambled block is mixed (XORed) with your plaintext block. Because Block 5 only needs the number 5 to do its job and does not have to wait for Blocks 1 through 4 to finish, a modern computer processor can lock or unlock dozens of blocks at the exact same time!
5. Galois/Counter Mode (GCM)
Today, GCM is the gold standard mode of operation across the internet. Standard encryption modes like CBC and CTR hide your message so hackers cannot read it, but they do not stop a hacker from blindly flipping bits in the locked message to corrupt your data.
GCM combines fast Counter (CTR) mode encryption with a special math check called an authentication tag (or integrity check). When the receiver unlocks a file protected by GCM, the mode checks the tag first. If a hacker changed even a single bit of the locked file while it was traveling across the internet, GCM spots the tampering immediately and rejects the damaged file.
Popular Examples Of Block Ciphers
Over the last five decades, cryptographers have built many block ciphers. As computers grew millions of times faster, older ciphers retired and stronger ones took their place. Here are the five most famous block ciphers in history.
1. Data Encryption Standard (DES)
Adopted by the United States government in 1977, DES was the first block cipher used by banks and businesses around the world. Built on a 16-round Feistel network, DES locked data in 64-bit blocks using a 56-bit secret key. In the 1970s, a 56-bit key seemed strong enough. However, a 56-bit key only has about 72 quadrillion possible combinations. By the late 1990s, special computers were built that could test every single DES key and unlock a message in less than 24 hours. Today, DES is completely insecure and only studied for history.
2. Triple DES (3DES)
When computers became fast enough to break DES in the late 1990s, banks and payment networks needed an immediate upgrade without rebuilding all their hardware from scratch. The solution was Triple DES (3DES). Triple DES takes each 64-bit block of data and runs it through the old DES engine three times in a row: it locks the block with Key 1, runs the reverse process with Key 2, and locks it again with Key 3. This raised the effective key strength up to 112 or 168 bits. While 3DES kept financial systems safe for two decades, running a cipher three times made it very slow, and its smaller 64-bit block size eventually showed weaknesses. Today, 3DES has been retired in favor of AES.
3. Advanced Encryption Standard (AES)
In 1997, the United States National Institute of Standards and Technology (NIST) held a global contest to find a brand-new, ultra-fast block cipher to replace DES. After years of testing by the world’s sharpest mathematicians, a cipher named Rijndael (created by Belgian cryptographers Joan Daemen and Vincent Rijmen) won the contest in 2001 and became the Advanced Encryption Standard (AES).
AES uses a 128-bit block size and an SPN internal design. It comes in three flavors based on the secret key length you choose:
- AES-128: Uses a 128-bit key and runs 10 rounds of scrambling.
- AES-192: Uses a 192-bit key and runs 12 rounds of scrambling.
- AES-256: Uses a 256-bit key and runs 14 rounds of scrambling.
Today, AES is built directly into the silicon chips of almost every smartphone, laptop, and server on Earth, making it lightning fast and practically unbreakable.
4. Blowfish
Created in 1993 by security expert Bruce Schneier, Blowfish was designed as a fast, free alternative to DES that anyone could use without paying patent fees. It uses a 64-bit block size, a 16-round Feistel network, and a flexible key length anywhere from 32 bits up to a massive 448 bits. While Blowfish is still famous for password hashing tools, even its creator now recommends moving to newer 128-bit block ciphers because of Blowfish’s small 64-bit block size.
5. Twofish
Twofish is the younger, stronger sibling of Blowfish, also co-designed by Bruce Schneier. It was one of the top five finalists in the NIST competition that selected AES. Twofish uses a full 128-bit block size, a 16-round Feistel structure, and keys up to 256 bits long. It remains highly secure and is still used in several file and disk encryption tools today.
Comparison Table
To help you clearly see how the five most famous block ciphers compare to one another, and how a block cipher differs from a stream cipher, review the comparison tables below.
| Block Cipher Name | Year Created | Block Size | Key Size Options | Number of Rounds | Internal Design | Current Security Status |
| DES | 1977 | 64 bits | 56 bits | 16 rounds | Feistel Network | Broken and unsafe (key is too small) |
| Triple DES (3DES) | 1998 | 64 bits | 112 or 168 bits | 48 DES-equivalent rounds | Feistel Network | Retired and slow (replaced by AES) |
| Blowfish | 1993 | 64 bits | 32 to 448 bits | 16 rounds | Feistel Network | Aging (64-bit block is too small for big files) |
| Twofish | 1998 | 128 bits | 128, 192, or 256 bits | 16 rounds | Feistel Network | Very safe and strong |
| AES | 2001 | 128 bits | 128, 192, or 256 bits | 10, 12, or 14 rounds | Substitution-Permutation (SPN) | Worldwide gold standard (fast and unbreakable) |
Here is a quick side-by-side look at how a Block Cipher compares to its cousin, the Stream Cipher:
| Feature | Block Cipher | Stream Cipher |
| How It Locks Data | Cuts data into fixed-size blocks (64 or 128 bits) and locks one block at a time | Locks data one tiny bit or byte at a time in a non-stop stream |
| Padding Required? | Yes (adds filler bits if the final block is not completely full) | No (locks the exact number of bits you have with zero waste) |
| Core Math Principles | Uses both Confusion (swapping) and Diffusion (shuffling) | Relies mainly on Confusion (mixing plaintext with a key stream) |
| Best Everyday Use | Locking files, hard drives, databases, and general internet traffic | Fast mobile connections, live voice or video streams, and low-power chips |
Where Do You Use Block Ciphers In Daily Life?
Even if you have never heard the words “block cipher” before reading this guide, you use them dozens of times every single day without pressing a special button:
- Browsing Secure Websites (HTTPS): Whenever you see the padlock icon in your web browser address bar while shopping or banking, your browser is likely using AES in GCM mode to lock the pages and forms going back and forth between your screen and the website server.
- Locking Your Phone and Laptop: Both Apple iPhones (FileVault and iOS Data Protection) and Windows laptops (BitLocker) use the AES block cipher to lock every photo, app, and document stored on your device. If someone steals your phone, they cannot pull out the memory chip and read your files.
- Home Wi-Fi Networks: When you type in your home Wi-Fi password using modern WPA2 or WPA3 security, your router uses the AES block cipher to scramble all wireless data flying through the air between your phone and your router.
- Private Messaging Apps: Apps that promise end-to-end encryption, such as WhatsApp and Signal, use the AES block cipher to lock your text messages, voice notes, and photos on your phone before they ever touch the company’s servers.
- Password Managers: When you store all your website logins inside a password vault, password mnagers lock your entire vault file using AES-256 so that only your master password can open it.
Conclusion
A block cipher is one of the most important inventions of the computer age. By slicing your digital messages and files into fixed-size blocks, filling any leftover gaps with padding, and running each block through multiple rounds of key mixing, byte swapping, and bit shuffling, a block cipher turns your private life into an unbreakable code for outsiders. While early designs like DES helped pave the way, modern block ciphers like AES paired with smart modes of operation like GCM protect almost everything we do online today. The next time you tap your credit card, send a private family photo, or log into your bank account, you can feel confident knowing that the simple, powerful math of block ciphers is working quietly to keep your data safe.
Frequently Asked Questions
1. What Is The Main Difference Between A Block Cipher And A Stream Cipher?
A block cipher chops data into fixed-size chunks (usually 128 bits) and scrambles one whole chunk at a time through multiple rounds of mixing. A stream cipher scrambles data one single bit or byte at a time like water flowing through a pipe, without waiting for a full block or adding padding.
2. Is AES A Block Cipher?
Yes, the Advanced Encryption Standard (AES) is the most widely used block cipher in the world today. It locks data in fixed 128-bit blocks using secret keys that are 128, 192, or 256 bits long.
3. Why Do Block Ciphers Need Padding?
Block ciphers can only process blocks that match their exact size, such as 16 bytes (128 bits). Because most real messages do not divide evenly into groups of 16 bytes, padding adds extra filler bytes to the end of the final block so it is completely full before locking begins.
4. Which Block Cipher Mode Of Operation Is The Safest To Use?
Galois/Counter Mode (GCM) is widely considered the best and safest mode for most modern needs. It is very fast because it can lock multiple blocks at the same time, and it includes a built-in safety tag that alerts you if a hacker tries to alter the locked data.
5. Why Is Electronic Codebook (ECB) Mode Considered Unsafe?
ECB mode locks every block the exact same way without linking them together or using a random starting number. Because of this, two identical blocks of original data always produce two identical blocks of locked data, leaving visible patterns that hackers can easily spot.
6. Can A Hacker Break A Modern Block Cipher Like AES-256?
No. With our current technology, breaking AES-256 by guessing keys is mathematically impossible. There are so many possible 256-bit keys that even if every computer on Earth worked together for billions of years, they could not guess a single properly generated AES-256 key.
7. Does A Block Cipher Use One Key Or Two Keys?
A block cipher is a symmetric cipher, which means it uses one shared main secret key. Both the sender who locks the message and the receiver who unlocks the message use that exact same secret key.